Cybercriminals do not need to compromise every system in an organisation. They only need to find one unpatched server, exposed cloud resource, weak password, insecure application programming interface, misconfigured firewall or overlooked business-logic flaw.
As businesses across Kenya and Africa adopt cloud computing, mobile applications, digital payments, remote working and interconnected platforms, their potential attack surfaces continue to expand. A security control that worked six months ago may no longer protect an organisation from emerging vulnerabilities, configuration changes or newly discovered attack methods.
That is why organisations need more than antivirus software and automated vulnerability scans. They need a structured Vulnerability Assessment and Penetration Testing, commonly known as VAPT, programme that identifies security weaknesses, validates their business impact and provides a clear remediation roadmap.
Fanan Limited delivers professional Vulnerability Assessment and Penetration Testing services to organisations in Kenya and across Africa. Our approach helps businesses understand their actual exposure, prioritise the vulnerabilities that matter most and strengthen their security before malicious attackers exploit existing weaknesses.
Vulnerability Assessment and Penetration Testing are closely related cybersecurity services, but they perform different functions.
A vulnerability assessment systematically examines an organisation’s systems, applications, networks and infrastructure to identify known security weaknesses.
The assessment may detect issues such as:
The identified weaknesses are analysed and assigned risk ratings based on factors such as exploitability, technical severity, affected assets and potential business impact.
Penetration testing goes beyond identifying possible vulnerabilities. It involves controlled and authorised attempts to exploit security weaknesses to determine whether they can be used to compromise an organisation’s systems, applications, accounts or sensitive information.
A penetration tester approaches the target from an attacker’s perspective while operating within an agreed scope and documented Rules of Engagement.
The objective is not to disrupt business operations. It is to safely demonstrate:
Recognised methodologies treat penetration testing as a structured engagement covering pre-engagement activities, intelligence gathering, threat modelling, vulnerability analysis, exploitation, post-exploitation and reporting. The OWASP Foundation also recommends security-testing guidance tailored to web and cloud services, mobile applications and firmware. [wstg.owasp.org]
Although the two services complement each other, they should not be treated as identical.
| Area | Vulnerability Assessment | Penetration Testing |
|---|---|---|
| Primary purpose | Identify and classify weaknesses | Safely exploit and validate weaknesses |
| Coverage | Broad examination of in-scope assets | Deeper testing of selected attack paths |
| Automation | Uses automated tools supported by expert validation | Relies heavily on manual testing and expert analysis |
| Output | Prioritised vulnerability register | Validated findings, evidence and attack scenarios |
| Main question | What vulnerabilities exist? | What can an attacker achieve by exploiting them? |
| Recommended use | Routine security monitoring and baseline assessment | Periodic assurance, pre-launch testing and compliance |
An automated scan can identify a potentially vulnerable component, but it may not determine whether the vulnerability is exploitable within the organisation’s specific environment.
Human-led penetration testing can identify weaknesses that automated scanners frequently miss, including:
The most effective VAPT engagement therefore combines automated security tools with manual analysis, validation and controlled exploitation.
Africa’s rapid digital transformation has created significant opportunities for businesses, governments and consumers. It has also created new opportunities for cybercriminals.
The INTERPOL Africa Cyberthreat Assessment Report describes cyber threats affecting the continent as transnational, fast-moving and increasingly sophisticated, with financial systems, public services, critical infrastructure and public trust among the potential targets. [interpol.int]
Organisations in Kenya and across Africa face risks including:
VAPT helps an organisation move from assumed security to evidence-based security. Rather than waiting for an external attacker to expose a weakness, an authorised security team finds and helps correct it first.
Fanan Limited provides VAPT services covering on-premises, cloud-based and hybrid environments.
Our network vulnerability assessment examines internal and external infrastructure for weaknesses that may enable unauthorised access, malware deployment, privilege escalation or lateral movement.
Testing may cover:
We examine exposed services, vulnerable software versions, insecure protocols, weak configurations and access-control gaps. Findings are manually reviewed to reduce false positives and provide practical remediation guidance.
External penetration testing simulates an attacker attempting to compromise an organisation from the internet.
The testing may include:
The engagement identifies weaknesses that could be discovered and exploited without prior access to the organisation’s internal network.
Internal penetration testing evaluates what could happen if an attacker gained internal access through a compromised employee device, stolen credentials, malicious insider or insecure remote connection.
The assessment examines:
This testing helps determine whether one compromised account or endpoint could lead to a wider organisational breach.
Web applications are often exposed to customers, employees, suppliers and the public. A single application flaw can create a direct route to customer information, financial transactions or internal systems.
Our web application penetration testing covers weaknesses associated with:
Our testing is informed by the OWASP Foundation Web Security Testing Guide and applicable risk scenarios. The guide organises testing into areas such as identity, authentication, authorisation, session management, input validation, cryptography, business logic and client-side security. [jacobianen...eering.com], [wstg.owasp.org]
Mobile applications may store or transmit personal, financial and commercially sensitive information. They may also communicate with insecure backend services or expose sensitive functionality through poorly protected APIs.
Our mobile application testing can cover Android and iOS applications, including:
The assessment considers both the mobile application and the supporting backend environment.
APIs connect mobile applications, web platforms, payment systems, cloud services and third-party solutions. Weak API security can allow attackers to access records, perform unauthorised transactions or extract large volumes of data.
Our API penetration testing assesses:
Testing may cover REST, SOAP and GraphQL APIs, depending on the client environment.
Cloud services can be secure while still being configured insecurely by the customer. Cloud security testing helps identify weaknesses across platforms such as Microsoft Azure, Amazon Web Services and Google Cloud.
Our cloud assessment may examine:
Cloud testing is performed within the applicable provider’s testing policies and the client’s approved Rules of Engagement.
Weak wireless security may provide attackers with a route into internal systems without requiring physical network access.
Wireless testing may assess:
Technology is only one part of organisational security. Social engineering assessments evaluate whether attackers could manipulate employees into disclosing credentials, opening malicious files or granting unauthorised access.
Subject to written authorisation, testing may include:
These exercises are carefully planned to protect employees, avoid unnecessary disruption and provide measurable awareness improvements.
Some security risks are not caused by a single software vulnerability. They result from architectural decisions, excessive trust relationships or weak configurations.
Our review can cover:
Our methodology is designed to produce repeatable, defensible and actionable results.
We define the exact testing boundaries before technical work begins.
This stage establishes:
Testing is conducted only with documented client authorisation.
We collect information about the approved target environment to understand its technologies, exposed services and possible attack paths.
Activities may include:
We use appropriate commercial, open-source and manual techniques to identify vulnerabilities and configuration weaknesses.
Potential tools may include technologies such as:
Tool selection depends on the agreed scope and target environment. Automated findings are reviewed by security professionals rather than being transferred directly into a report without validation.
Our testers manually verify findings and, where authorised, perform safe controlled exploitation.
Manual validation helps distinguish real risks from:
Where exploitation is permitted, we gather only the evidence necessary to demonstrate impact.
Each confirmed finding is evaluated according to technical severity and business context.
The analysis may consider:
This provides better prioritisation than relying on automated scanner severity alone.
A professional VAPT report should support both executive decision-making and technical remediation.
Our reports may include:
The executive section explains risk in business language, while the technical section provides the information required by system administrators, developers and security teams.
Finding vulnerabilities is not the final objective. The real value comes from correcting them and confirming that the remediation is effective.
After the client implements corrective actions, Fanan Limited can conduct a retest to:
We tailor the testing approach to the engagement objectives.
The tester receives little or no prior information about the target.
This approach simulates an external attacker but may require more time for reconnaissance and may provide less coverage within a limited testing window.
The tester receives limited information or standard user access.
This approach provides a practical balance between attacker realism, cost and technical coverage. It is often appropriate for testing authenticated applications and role-based access controls.
The tester receives detailed system information, credentials, architecture documentation or source-code access.
This approach provides deeper and more efficient coverage. It is suitable where the primary objective is assurance rather than simulating an unknown external attacker.
VAPT can support compliance by demonstrating that an organisation regularly tests its technical controls and takes reasonable steps to protect information.
Kenya’s cybersecurity and privacy environment includes the Data Protection Act, the Data Protection Regulations, the Computer Misuse and Cybercrimes Act and the National Cybersecurity Strategy 2022–2027. The National Computer and Cybercrimes Co-ordination Committee identifies the National Cybersecurity Strategy as Kenya’s roadmap for a secure digital ecosystem and also provides official references relating to critical information infrastructure. [nc4.go.ke]
Under Kenya’s data-protection framework, organisations processing personal information are expected to implement appropriate technical and organisational safeguards. Regular testing of security measures helps an organisation identify whether those controls remain effective as systems and threats change. [olmllp.com], [securebits.africa]
Depending on the organisation and its sector, a VAPT engagement may also support assurance activities related to:
VAPT does not automatically make an organisation compliant. However, it provides evidence of technical due diligence and helps identify security gaps that could undermine compliance.
VAPT is valuable for organisations of every size, especially those that process sensitive data, support critical operations or deliver internet-facing services.
This includes:
A common baseline is to conduct a comprehensive penetration test at least annually, supported by more frequent vulnerability assessments. The appropriate frequency depends on risk, regulatory requirements and how often the environment changes.
Testing should also be considered:
High-risk organisations may conduct quarterly vulnerability assessments and annual or biannual penetration tests. Internet-facing applications with frequent deployments may need security testing integrated into the software-development lifecycle.
When comparing VAPT providers in Kenya or elsewhere in Africa, request a sample report with confidential information removed.
A credible report should contain:
A scanner-generated list without manual validation, business context or remediation guidance is not a complete penetration-testing report.
Fanan Limited understands the operational, regulatory and technology environments facing organisations in Kenya and other African markets. This allows our recommendations to reflect local realities while remaining aligned with recognised international security practices.
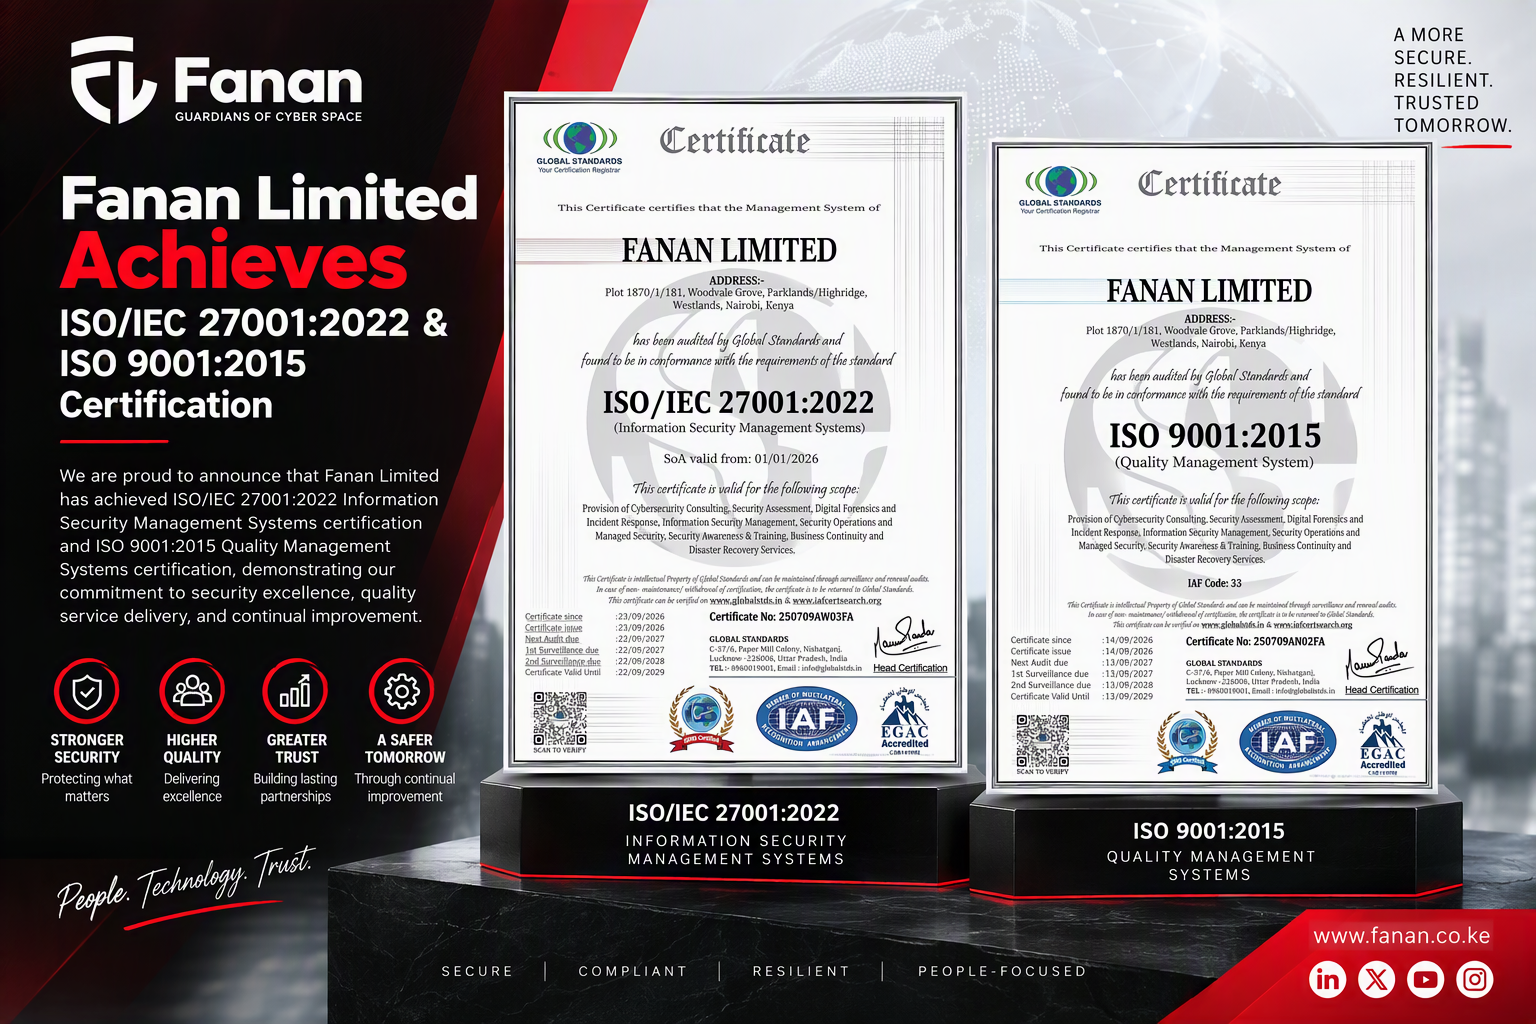
As an ISO 27001:2022 and ISO 9001:2015 certified organisation, Fanan Limited applies structured information-security and quality-management practices to our service delivery.
We do not prioritise findings solely because a scanner assigns them a high score. We consider the affected asset, available controls, exploitability and potential business impact.
Our VAPT engagements combine security tools with human-led analysis. This improves the accuracy of findings and supports the identification of business-logic vulnerabilities and attack chains.
Every confirmed vulnerability is accompanied by corrective recommendations. Where appropriate, we provide tactical fixes, configuration guidance and longer-term security improvements.
VAPT engagements can expose sensitive system details. We apply controlled access, secure evidence handling and agreed information-retention procedures throughout the engagement.
We help clients understand their findings and verify whether implemented corrective actions have resolved the identified weaknesses.
Our services can cover networks, websites, web applications, mobile applications, APIs, cloud environments, wireless networks and supporting infrastructure.
VAPT stands for Vulnerability Assessment and Penetration Testing. It combines broad vulnerability identification with controlled exploitation and manual validation.
A focused assessment may take approximately five to ten working days, while a broader multi-application or infrastructure engagement may require several weeks. The actual duration depends on the number of assets, application complexity, testing approach, user roles and reporting requirements.
Properly planned penetration testing is designed to minimise operational disruption. The Rules of Engagement define testing windows, prohibited techniques, escalation procedures and stop conditions. High-risk activities should only be performed with explicit approval.
No responsible cybersecurity provider should make that guarantee. VAPT provides a point-in-time assessment of the agreed scope. New vulnerabilities, configuration changes, compromised credentials and emerging attack techniques can alter the risk environment after testing.
No. Automated scanners are useful for identifying known technical weaknesses, but they may produce false positives and frequently miss business-logic flaws, chained vulnerabilities and context-specific access-control weaknesses. Manual validation is essential.
Yes. Fanan Limited can retest remediated findings and issue an updated report showing which vulnerabilities are closed, partially resolved or still open.
Yes. VAPT can provide evidence that technical-security controls are being assessed and help identify weaknesses relevant to ISO/IEC 27001 and PCI DSS. PCI guidance expects penetration testing to use an industry-accepted approach and to cover applicable network-layer and application-layer testing. [wstg.owasp.org]
The cost depends on the scope, number of systems, testing depth, application complexity and whether internal, external, cloud, API or mobile testing is required. A final quotation should follow a scoping exercise so the client pays for the required coverage rather than a generic package.
Every organisation has a digital attack surface. The important question is whether security weaknesses will be discovered first by an authorised cybersecurity professional or by a malicious attacker.
Fanan Limited helps organisations in Kenya and across Africa identify vulnerabilities, validate actual risks and implement practical corrective measures. Whether you require a network assessment, web application penetration test, API security review, mobile application test, cloud security assessment or a complete VAPT programme, our team can develop an engagement aligned with your environment and business objectives.
Protect your systems, applications and sensitive information with professional Vulnerability Assessment and Penetration Testing services.

Share This News